KOBIL mPower Cookie
KOBIL mPower Cookie
The main task is to authenticate the user based on the mPower JWT token.
Type
| Protocol | OpenID Connect 1.0 |
|---|---|
| HTTP method | GET |
| Type | Browser Flow |
| Endpoint | Authorization Endpoint |
| Flow Supported | Authorization code flow Implicit flow Hybrid flow |
| Response | ID Token, Access Token, Refresh Token |
How to configure
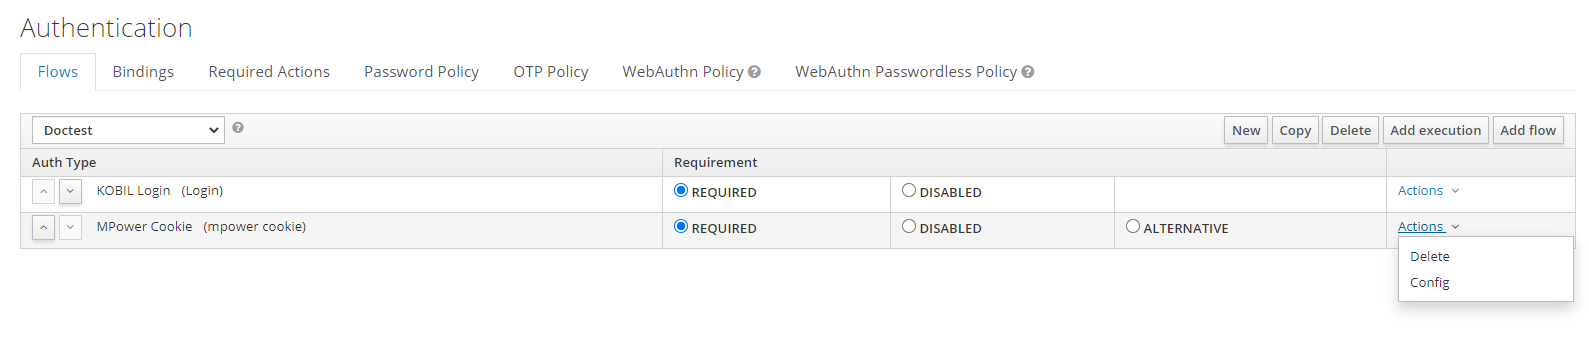
To access the config of the execution press the Actions button and select Config. The authenticator configuration screen will appear. Then enter your config data.
Configuration
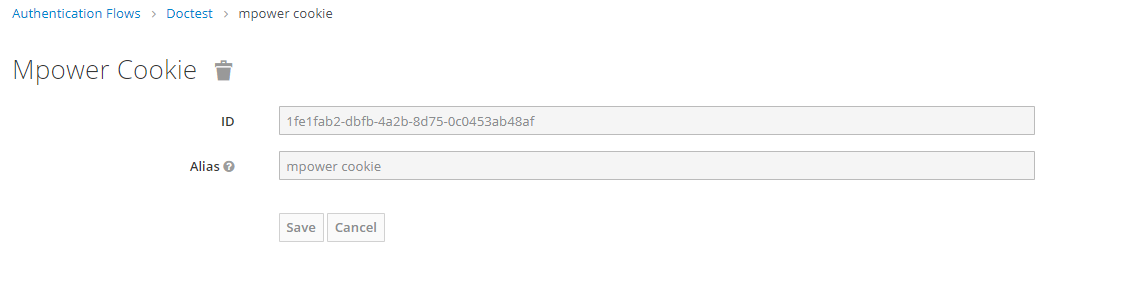
Parameters involved in KOBIL mPower Cookie execution
| Parameter | Description |
|---|---|
| Alias | Provide an alias name for the configuration to be set. |
User Flow
Execution Flow
This executions contains following main steps:
- KOBIL mPower Cookie must be preceded by another Authenticator since it procures a username from this precedent authenticator. For instance: KOBIL Login for user identification.
- User's identity is validated with KOBIL login.
- KOBIL mPower cookie flow is initiated as 2FA.
- The SSMS server verifies whether the saml_authorization cookie is available and validates it.
- If the cookie is valid, the user is logged in.