User Role Management
Introduction
Applications can provide access and permission to a role and assign that role to multiple Users to ensure that they have the same access and permission.
A role typically applies to one type of user. For instance, an organisation may include admin, manager, employee and user roles.
The following Roles can be selected (Single/Multiple) as per requirement:
- Create-Client
- Impersonation
- Manage-authorization
- Manage-claims
- Manage-clients
- Manage-events
- Manage-identity-providers
- Manage-realm
- Manage-users
- Query-clients
- Query-groups
- Query-realms
- Query-users
- View-authorization
- View-claims
- View-clients
- View-events
- View-identity-providers
- View-realm
- View-users
Super Admin Access
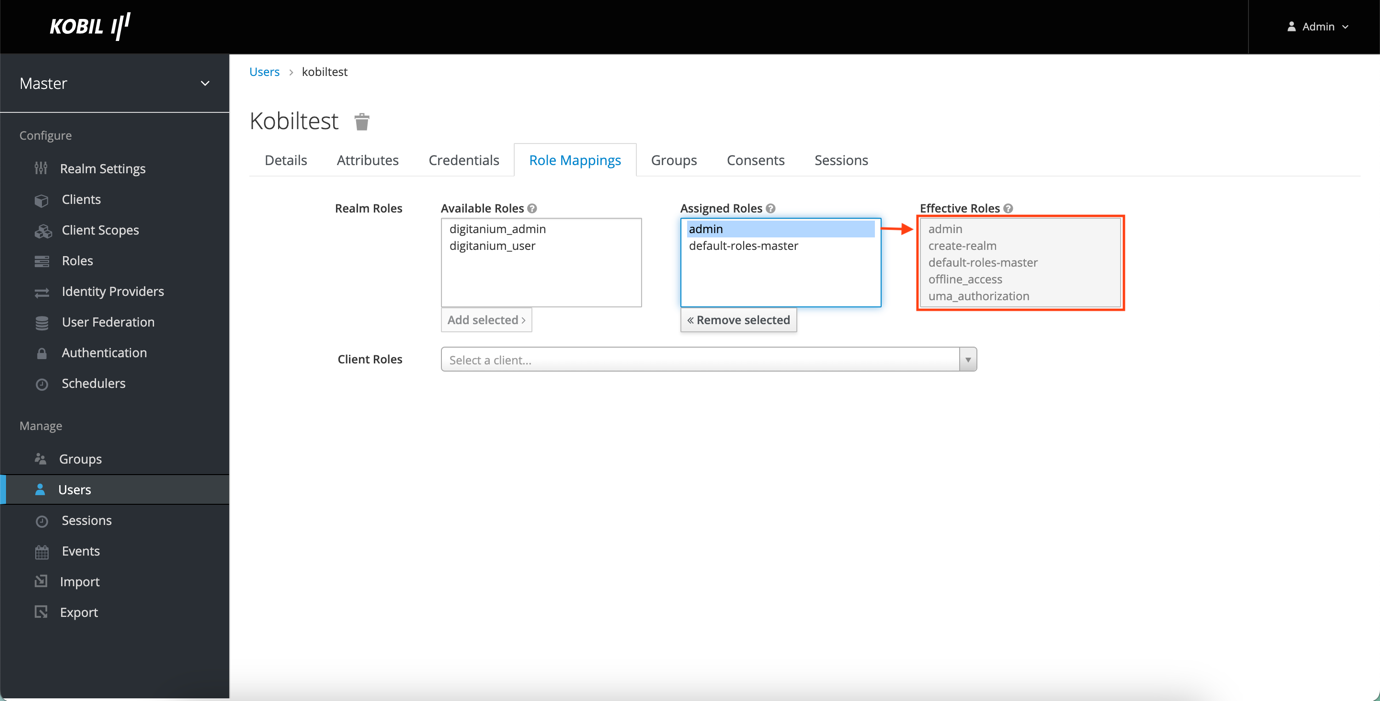
In the Master Tenant, when admin role is assigned to the User, the User becomes a Super Admin. With this Admin Role a User will act as a Super Admin with access to manage the entire IDP.
How to assign Admin Role:
Step 1: Navigate to the required User.
Step 2: Click on Role Mappings and select admin from the Available Roles.
Step 3: Press Add selected button.
Step 4: With this permission, the User will have access to all KOBIL IAM functions.
Admin Access
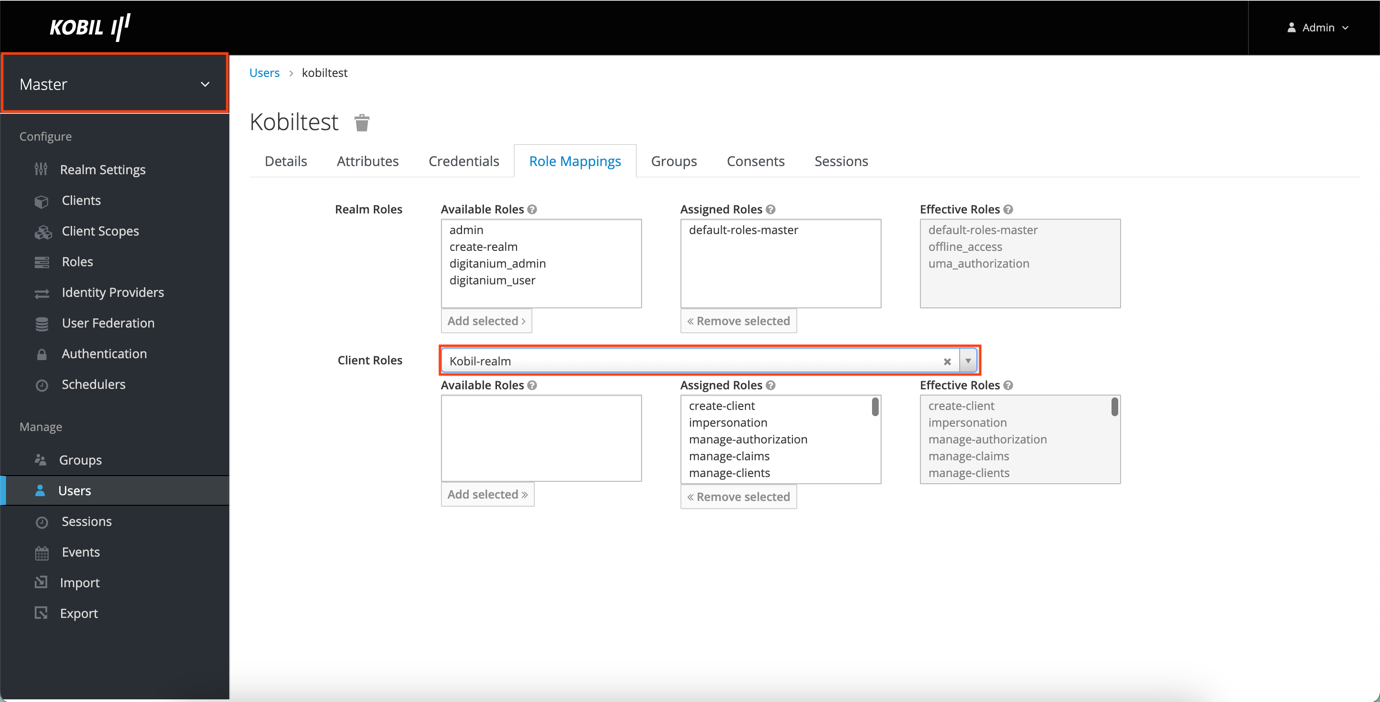
The User becomes Admin of the required tenant when all the roles are selected for the specific tenant. Admin Access can be set for a Tenant’s User in two ways.
1. Multiple Tenant access can be given to the user from the Master Tenant.
Procedure:
Step 1: Navigate to the required User.
Step 2: Click on Role Mapping -> Set the client roles to the required Tenant.
Step 3: Under Available Roles
- Select all from the dropdown list and click on Add selected button. This will allow the new User to have Admin access for the selected Tenant.
- Access points can also be selected individually based on the requirements.
2. Admin access can be given from the specific Tenant.
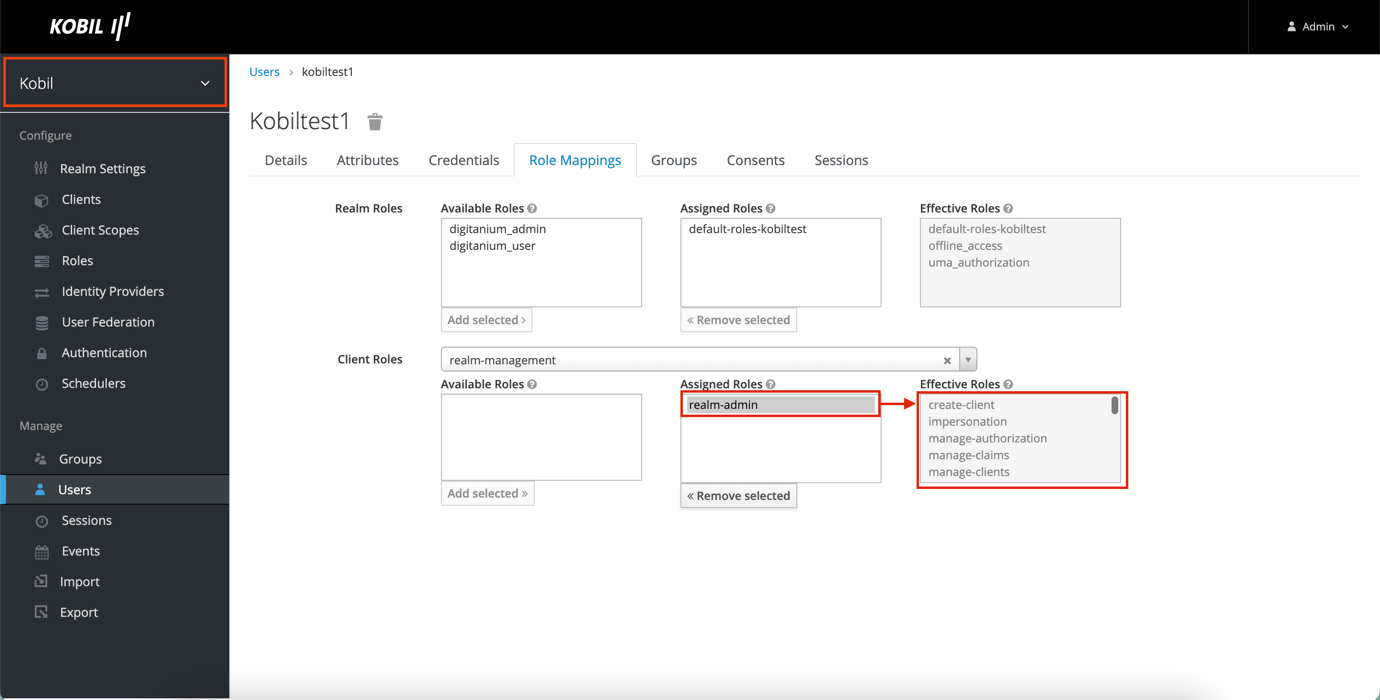
Procedure:
Step 1: Navigate to the required User.
Step 2: Navigate to Role Mappings -> Set the Client roles to realm-management.
Step 3: Under Available Roles, Select realm-admin.
Step 4: Click on Add selected. (NOTE: This will automatically give access to all the Roles available which makes the User to be Admin for the particular tenant.)
Step 5: Access points can also be selected individually based on requirements.
Composite Roles
It is a role that has one or more additional access associated with it. When a composite role is mapped to a User, the User will have the effective roles associated with the composite role.
How to add Composite Role:
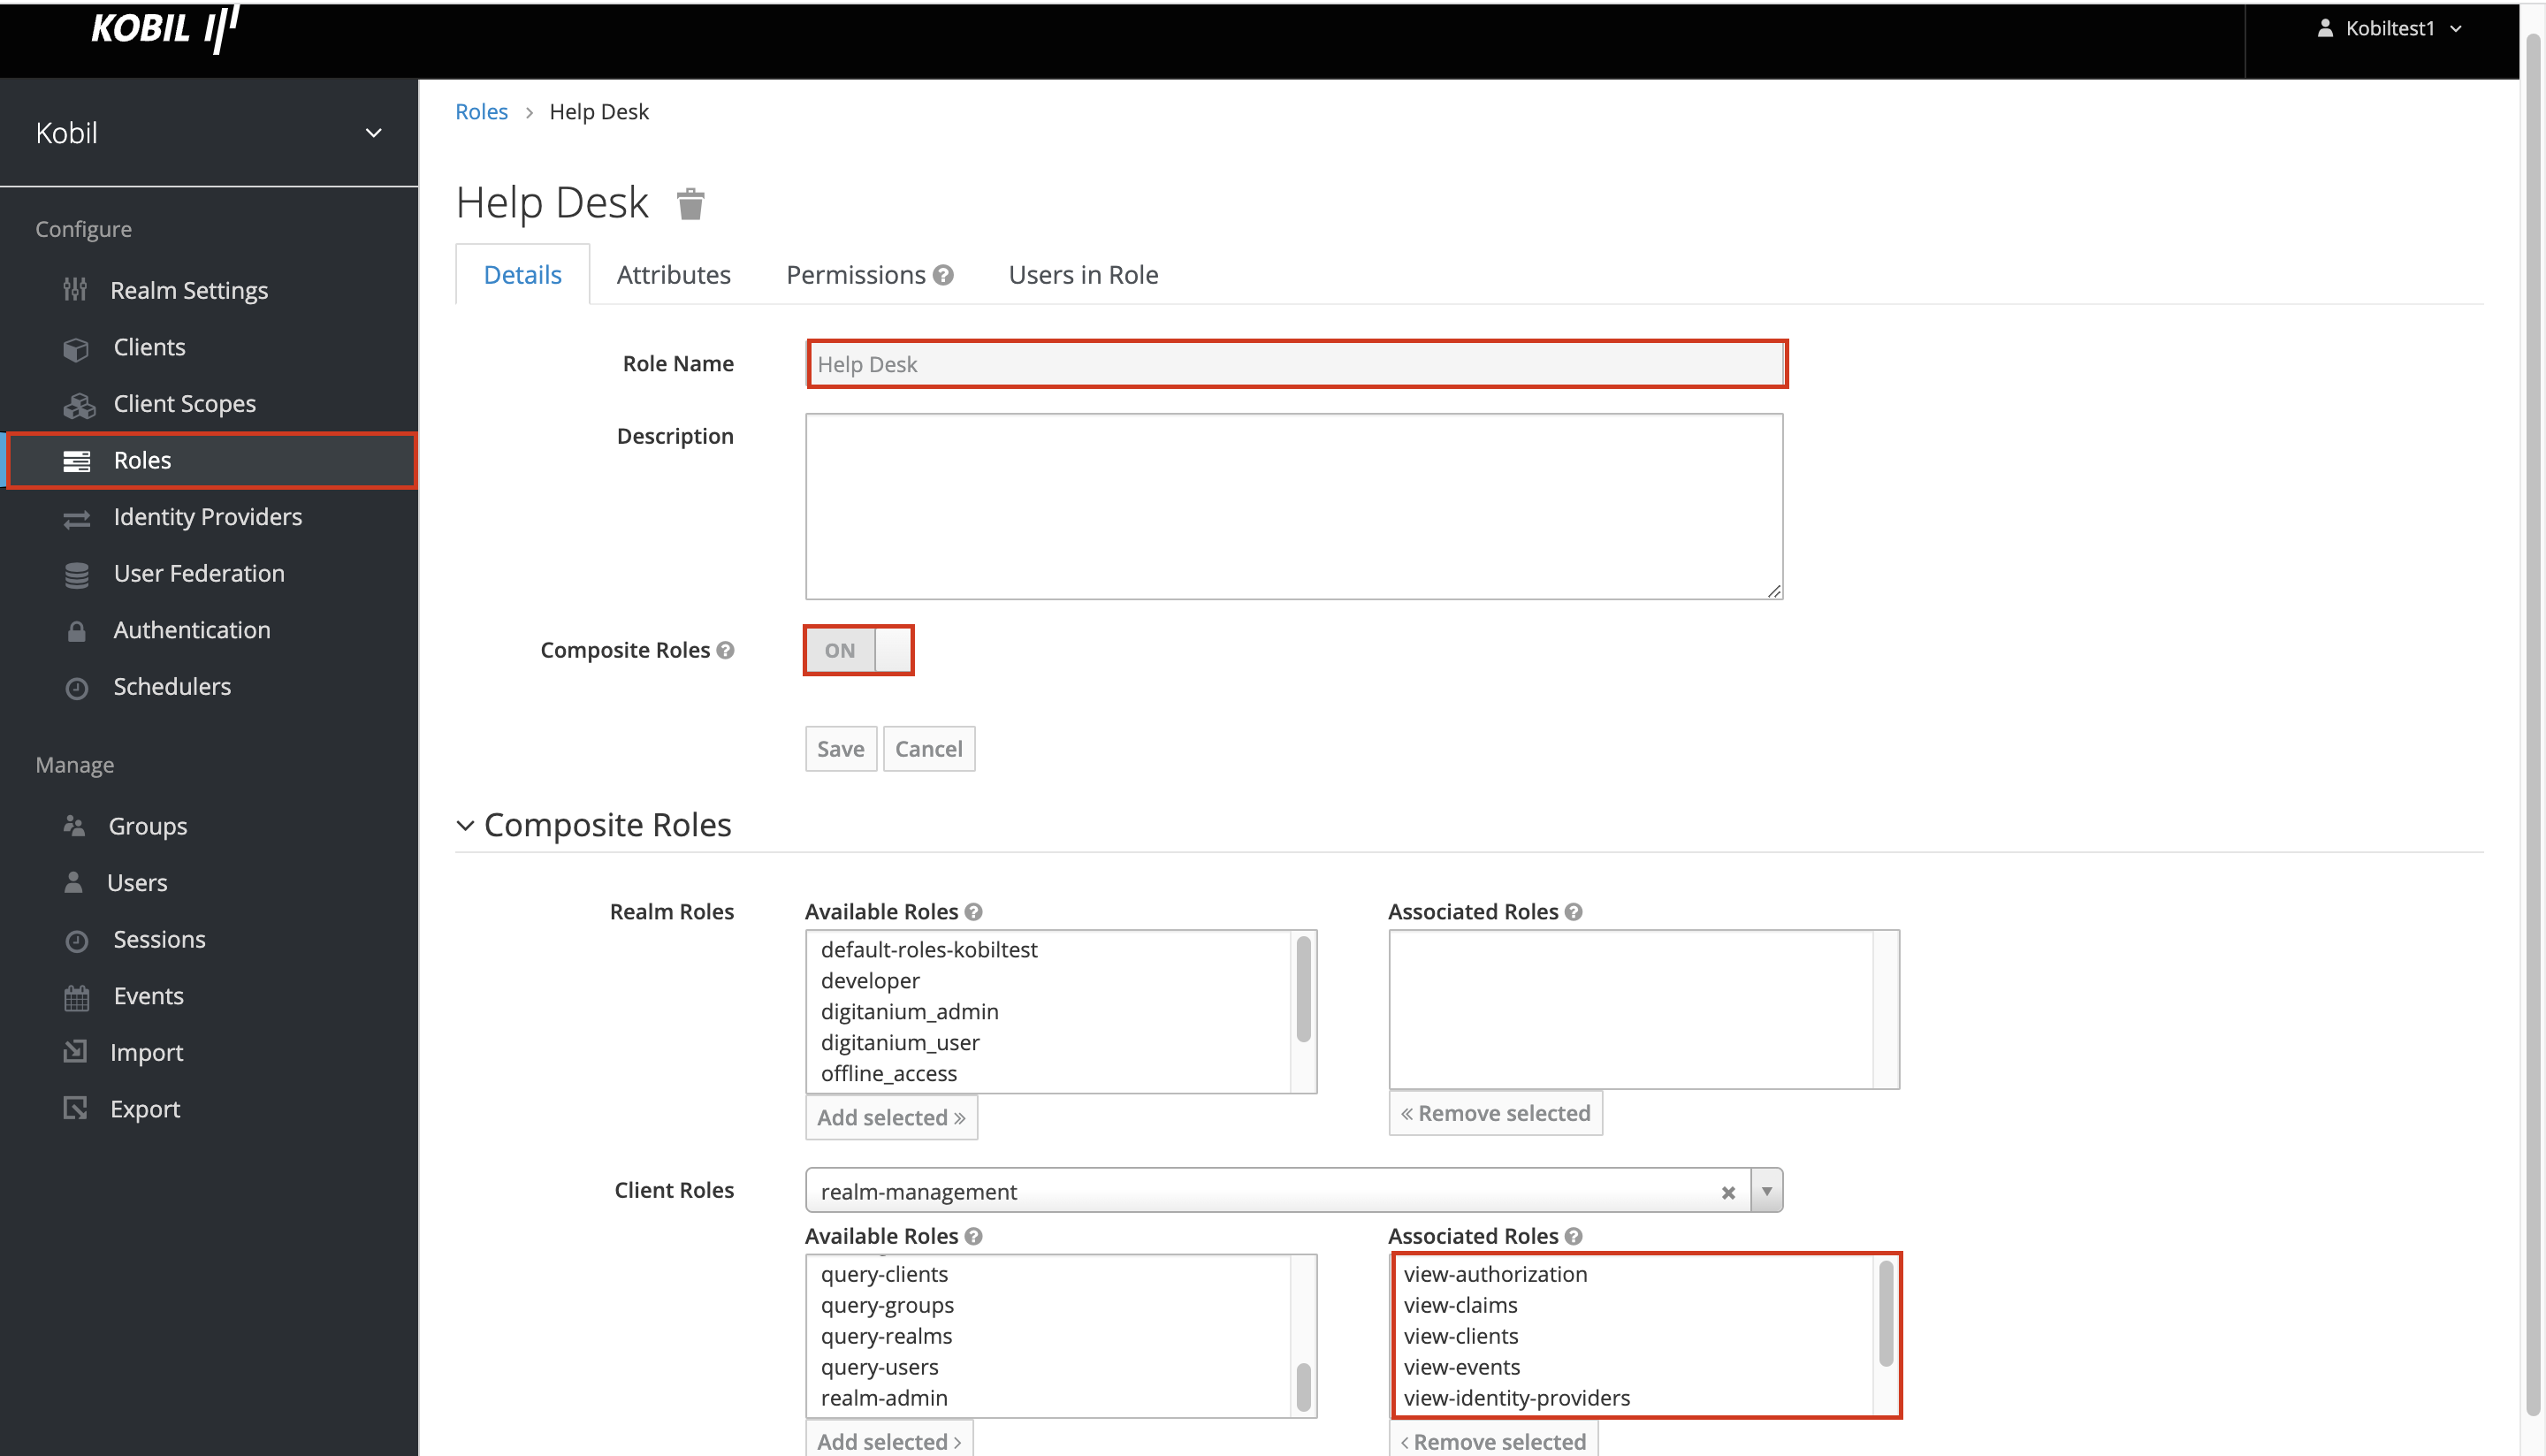
Step 1: Navigate to Roles under the Configure menu.
Step 2: Under Realm Roles, Click on Add Role.
Step 3: Enter the required Role Name.
Step 4: Toggle Composite Roles to ON.
Step 5: Realm Roles and Client Roles will be visible and the necessary access points can be selected.
Step 6: Click on Add selected. This will map the selected access to the created role.
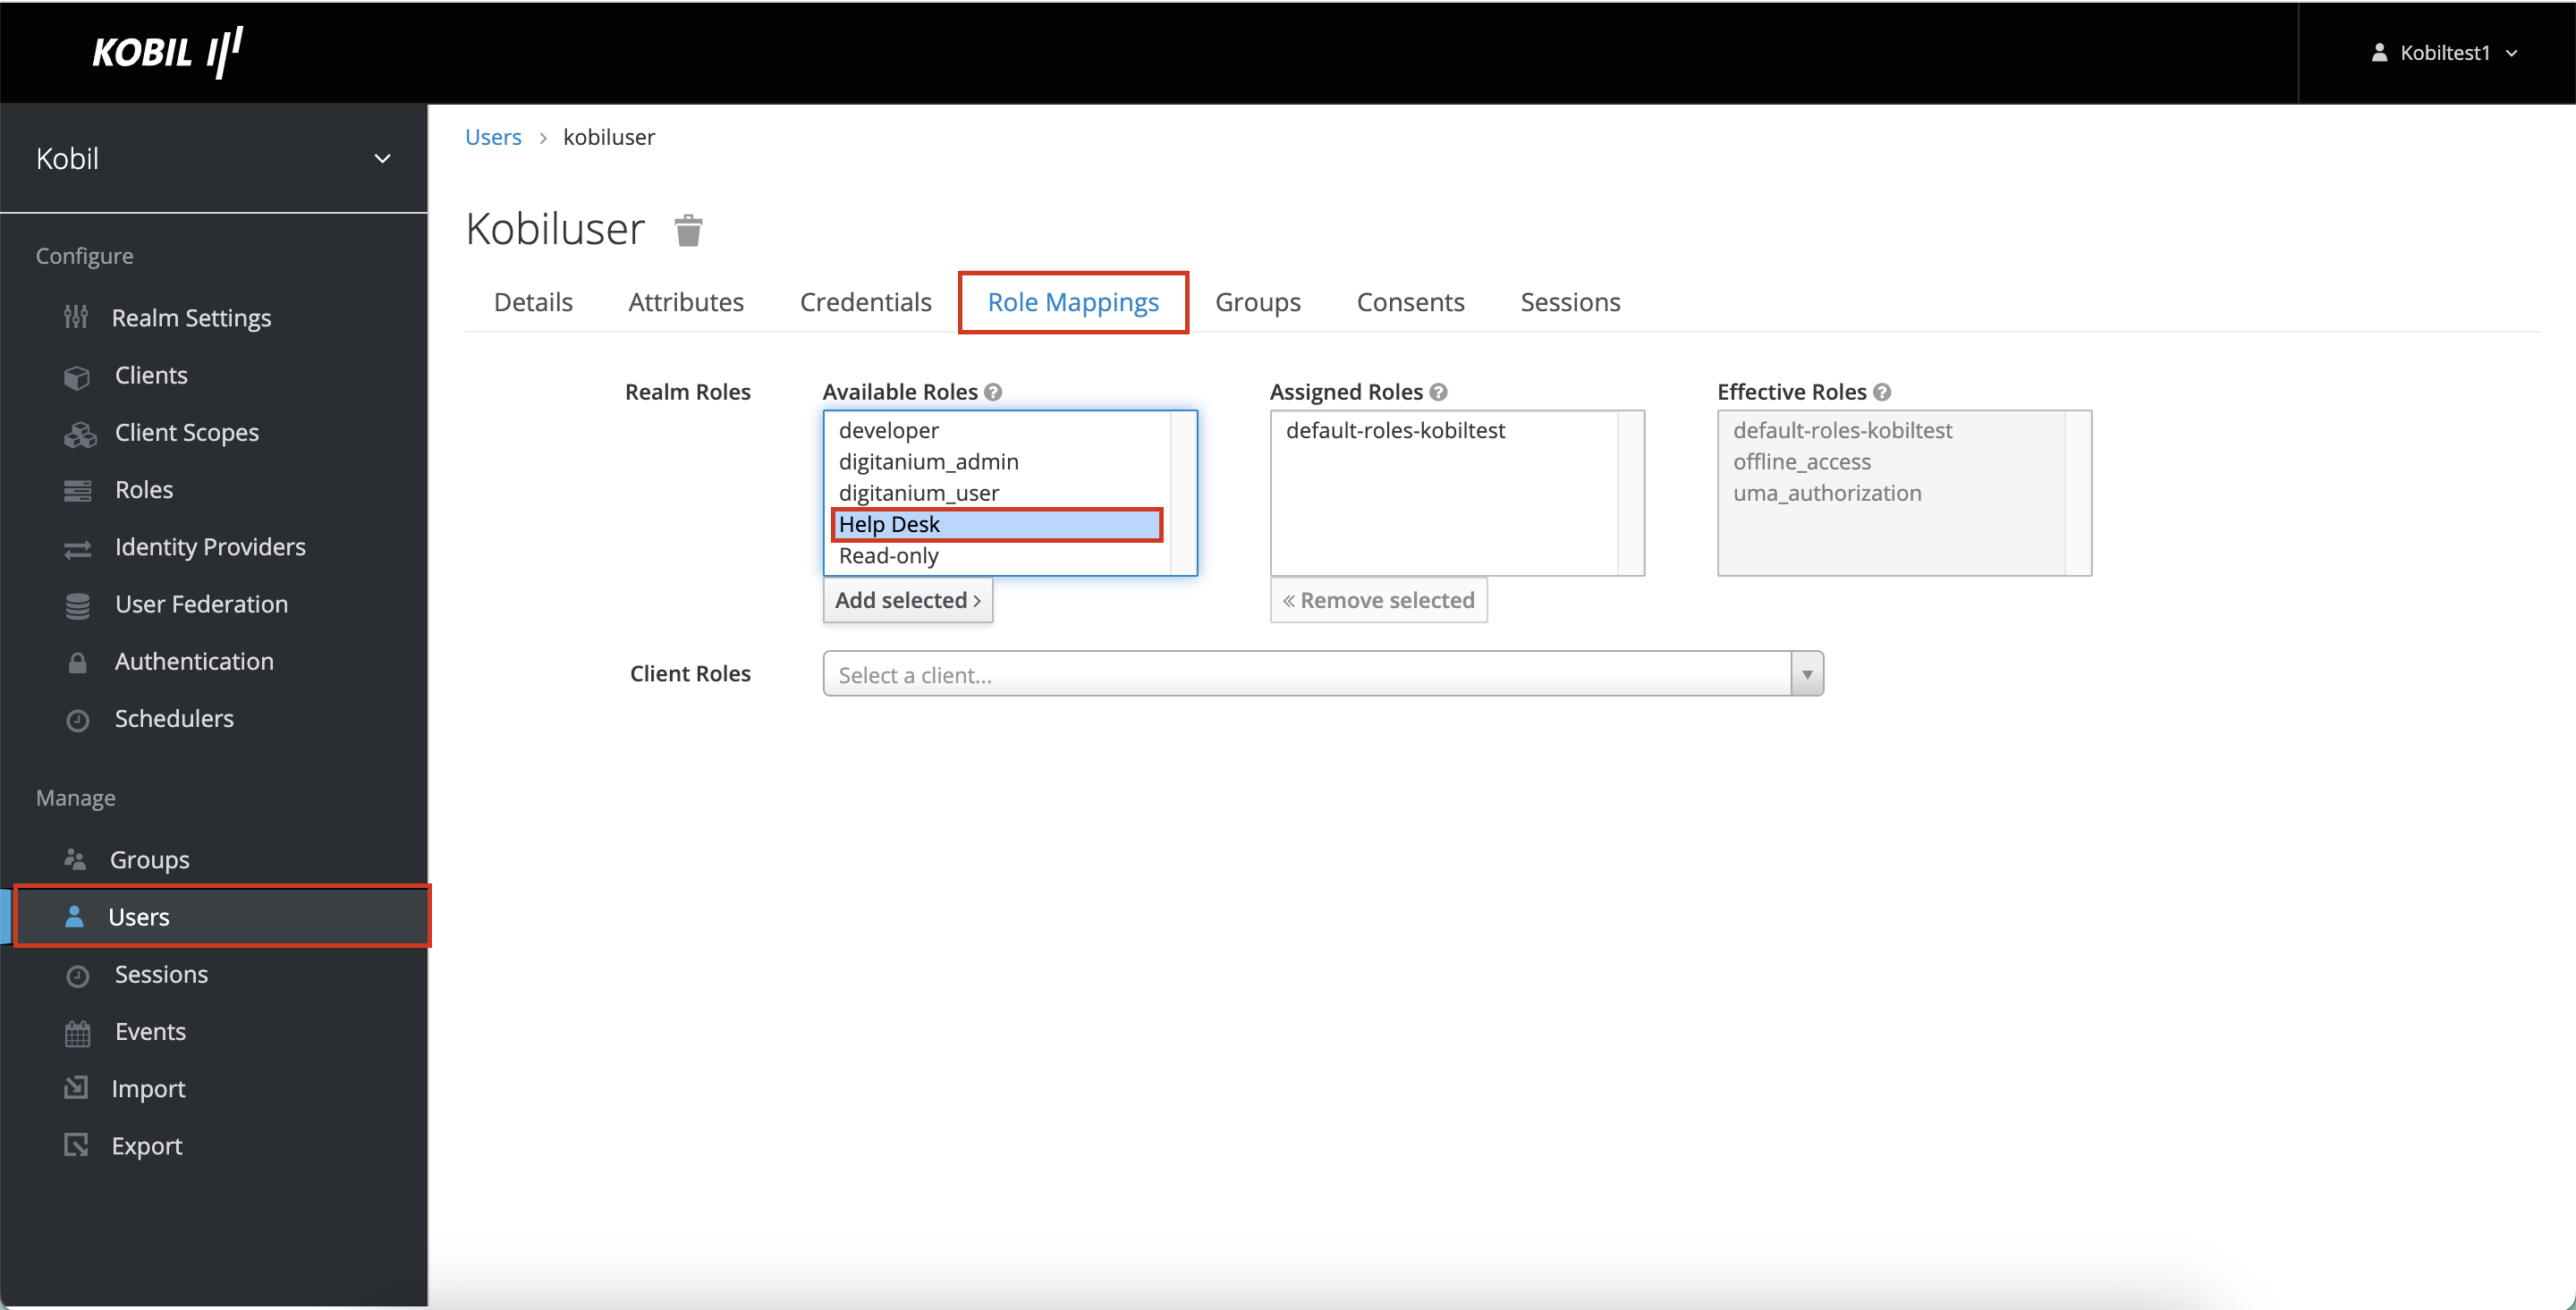
Step 7: This Role will be visible under the Role Mapping upon creating a new User.
For instance,
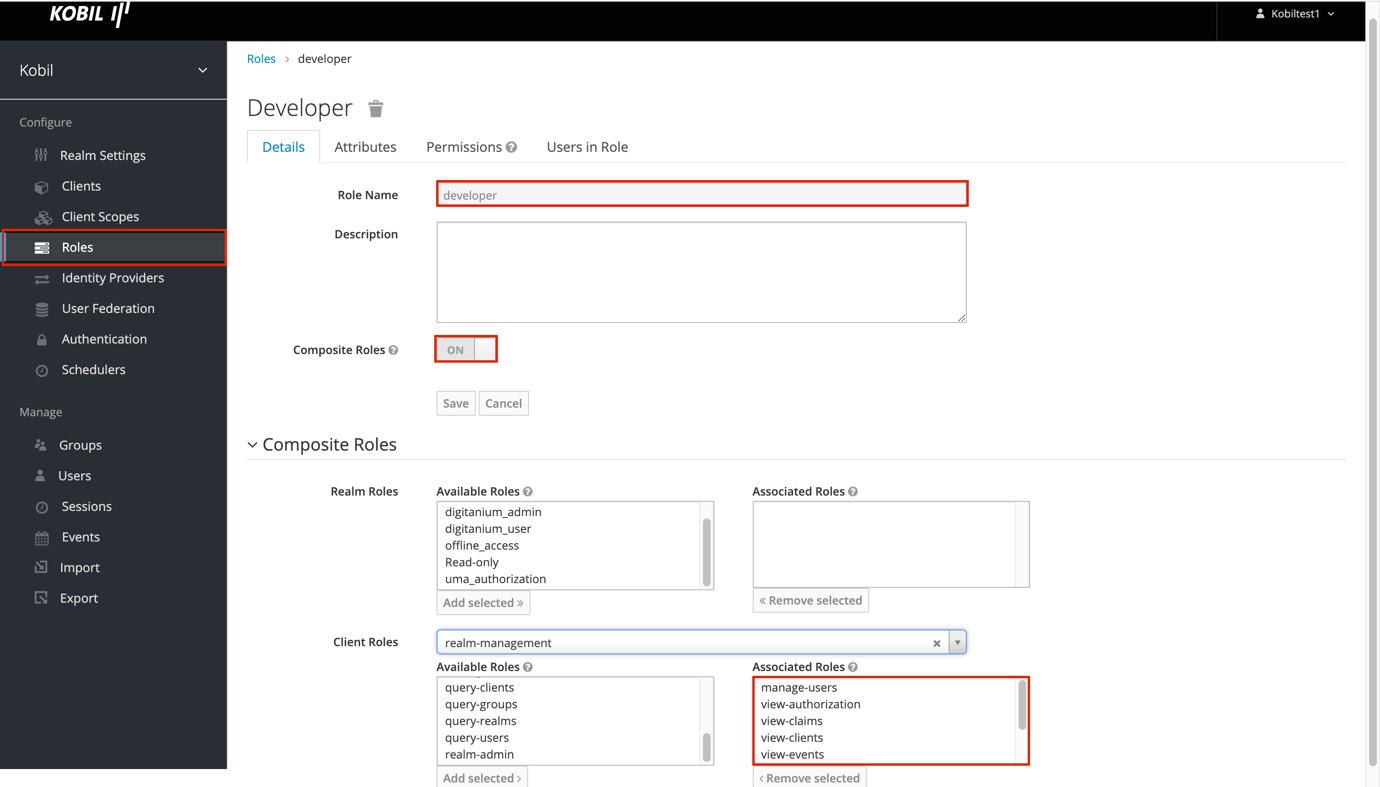
1. Developer Role:
With this role a User has complete view access along with Manage access for the required User. With Manage-users access, the user can create, update or delete any users in the Tenant.
Required Roles:
- View-authorization
- View-claims
- View-clients
- View-events
- View-identity-providers
- View-realm
- View-users
- Manage-users
- Create-clients
2. Help Desk:
With this role the User has complete view/read access in the Tenant.
Required Roles:
- View-authorization
- View-claims
- View-clients
- View-events
- View-identity-providers
- View-realm
- View-users
Under the Role Mappings tab while creating a new user, you can select the required role from the Available Roles.
The below table shows the different permission access for the roles created:
(*) - Only for the specific tenants the admin has access
| Permission | Super Admin | Admin | Developer | Help Desk |
|---|---|---|---|---|
| Create Tenant | • | |||
| Create Clients | • | • | • | |
| Manage Authorization | • | • | ||
| Manage Claims | • | • | ||
| Manage Clients | • | • | ||
| Manage Events | • | • | ||
| Manage Identity Providers | • | • | ||
| Manage Realm | • | * | ||
| Manage Users | • | • | • | |
| Query Clients | • | • | • | • |
| Query Groups | • | • | • | • |
| Query Realms | • | • | • | • |
| Query Users | • | • | • | • |
| View Authorization | • | • | • | • |
| View Claims | • | • | • | • |
| View Clients | • | • | • | • |
| View Events | • | • | • | • |
| View Identity Providers | • | • | • | • |
| View Realms | • | * | • | • |
| View Users | • | • | • | • |